
Slack Bot Token: Where to Find It, and xoxb vs xoxp Tested
A Slack bot token starts with xoxb- and acts as your app's bot user. Get one by creating an app at api.slack.com/apps, adding bot scopes under OAuth & Permissions, installing the app, and copying the Bot User OAuth Token. How it differs from xoxp user tokens, xapp app-level tokens, xoxe rotation and xoxc session tokens.
Your Slack bot token is the Bot User OAuth Token on your app's OAuth & Permissions page. It starts with xoxb-, acts as your app's own bot user, and shows up only after the app is installed to a workspace. To get one, create an app at api.slack.com/apps, add Bot Token Scopes such as chat:write under OAuth & Permissions, click Install to Slack, approve it, and copy the token from the OAuth Tokens box. Most code reads it from an environment variable named SLACK_BOT_TOKEN.
A user token starts with xoxp- and acts as the person who approved the app. Slack's docs recommend bot tokens for most apps, because they keep working if the installing user is deactivated. To set the same app up from a file, see our app manifest example. Installing through your own OAuth flow on localhost is covered in Slack OAuth redirect URL on localhost.
Some things only a user can do: a bot has its own presence and cannot set yours, for example. That is why tools that keep your own Slack dot green, like Slack Green, use your signed-in session rather than a bot token; the difference is covered in Slack xoxc and xoxd tokens.
We made a test app in our own workspace on 3 October 2026, installed it, took both tokens, ran them, then deleted the app. The screenshot and outputs below come from that run.
How to get a Slack bot token
- Go to
api.slack.com/apps, click Create New App, choose From scratch, name it and pick the workspace. - Open OAuth & Permissions and add Bot Token Scopes, for example
chat:writeto post andusers:readto read people and presence. - Click Install to Slack (older pages say Install to Workspace) and Allow. Some workspaces require an admin to approve new apps.
- Copy the Bot User OAuth Token (
xoxb-...) from the OAuth Tokens box on the same page and store it as a secret, never in code or a public repository. If one ends up in a repo anyway, revoke it and reinstall; a reinstall alone returns the same token. - Invite the bot to any channel it needs to post in:
/invite @your-bot. Without it, posts fail with not_in_channel in public channels and channel_not_found in private ones.
The api.slack.com/apps link now opens the settings at app.slack.com/app-settings/<workspace ID>/<app ID>/oauth. The token sits in a plain text field with a Copy button, with no reveal step, so anyone who can see your screen can read it. We hid ours in this capture:
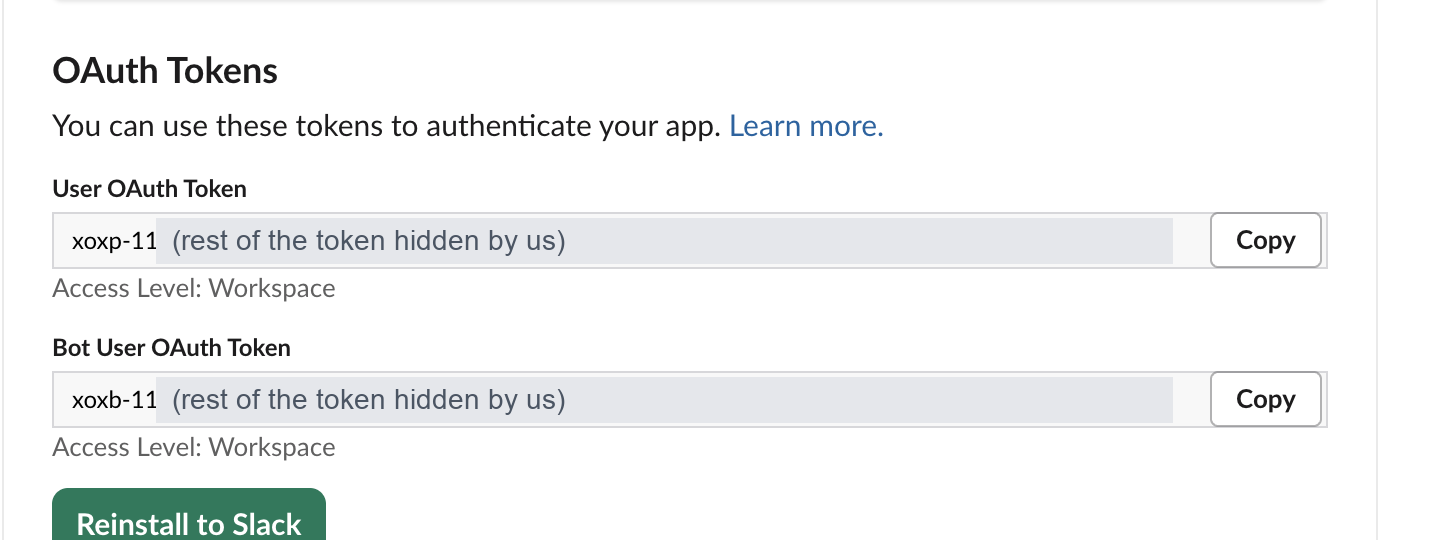
The page shows the same tokens every time you open it, so you can come back for a lost token. Clicking Reinstall to Slack without changing scopes also returned the same two tokens in our test.
When you add scopes later, reinstall the app so the token gets them. Until then, calls that need the new scope fail with missing_scope; the token string itself stays the same.
Test it:
curl -s -H "Authorization: Bearer $SLACK_BOT_TOKEN" https://slack.com/api/auth.testA bot token answers with a bot_id; a user token does not. That is the quickest way to tell which one you pasted.
A common first use of an xoxb- token is CI alerts. The workflow YAML for posting from a build, with threads and message updates, is in how to send a Slack message from GitHub Actions. From a Python script, the token goes into slack_sdk's WebClient; our tested scripts, with thread replies and the errors each mistake returns, are in send a Slack message from Python. Jenkins takes the same token in its Slack plugin, but slackSend needs botUser: true or every post fails with a 404 (our Jenkins test). In n8n, a bot token in a Slack API credential covers sending, history, reactions and uploads, but not setting a status (n8n Slack credentials).
What a real xoxb and xoxp token look like
Both tokens from our test app had the same first number, 11256386461409, which is also the first half of the app's client ID; it is the workspace's numeric ID. The rest differed in shape:
| Bot token | User token | |
|---|---|---|
| Prefix | xoxb- | xoxp- |
| Parts after the prefix | 3: two 14-digit numbers, then 24 letters and digits | 4: three 14-digit numbers, then 32 hex characters |
| Total length | 59 characters | 82 characters |
auth.test user | sgtokencheck, the bot user (U0C798V2M88) | sieun, the person who clicked Allow |
auth.test bot_id | B0C68LU08NP | none |
Reading the token from the environment variable most code uses, SLACK_BOT_TOKEN, in Python with slack_sdk:
import os
from slack_sdk import WebClient

client = WebClient(token=os.environ["SLACK_BOT_TOKEN"])
print(client.auth_test().data)
Each call below ran against the live API with the two tokens and with two broken ones:
| Call | Token | Result |
|---|---|---|
auth.test | xoxb | ok, with bot_id |
auth.test | xoxp | ok, no bot_id |
search.messages | xoxb | not_allowed_token_type |
search.messages | xoxp without search:read | missing_scope |
users.info on a person | either | ok |
auth.test | xoxb-123 (made up) | invalid_auth |
auth.test | no token | not_authed |
auth.test after we deleted the app | xoxb | account_inactive |
auth.test after we deleted the app | xoxp | token_revoked |
So not_allowed_token_type means the method does not accept this kind of token at all; no scope will fix it, and you need a user token. missing_scope means the token type is right but the app was not granted the scope.
Find a leaked Slack token in your code
People search for xoxp- together with config.json, config.ini, settings.py and config.yml because that is where tokens end up. To check your own repository before you push, this pattern matched every token shape above and nothing else in our test files:
grep -rEnI "(xox[abpe]|xapp)[.-][0-9A-Za-z.-]{10,}" .If it finds a live token, revoke it rather than only deleting the line; the token is still in your git history.
Slack token types and prefixes
| Prefix | Token | Acts as |
|---|---|---|
xoxb- | Bot token | Your app's bot user |
xoxp- | User token | The user who approved the app |
xapp- | App-level token | The app across all its installs |
xoxe.xoxb-, xoxe.xoxp- | Rotating access token | Bot or user, expires after 12 hours |
xoxe- | Refresh token | Used to get a new access token |
xwfp- | Workflow token | A workflow step, for at most 15 minutes |
xoxc-, xoxd- | Web client session | You, as the Slack web app |
Slack's docs also describe configuration tokens for the App Manifest APIs and service tokens for apps built with the Deno Slack SDK.
Never appear "away" on Slack again
Cloud-based. No downloads. Works 24/7 even when your laptop is off.
xoxb vs xoxp
users.profile.set for their own status, or reminders.add, whose reference lists only user-token scopes (what it still does is in Slack reminder bot).A user token also carries user scopes that the user approved. Slack's docs note that user token actions are performed as if by the user themselves. A bot token cannot do this: with as_user=true it still posted as the bot in our as_user test.
xoxe tokens and token rotation
If you turn on token rotation in your app settings, oauth.v2.access returns an access token with an xoxe. prefix that expires after 43,200 seconds (12 hours), plus a refresh token starting with xoxe-. Call oauth.v2.access with grant_type=refresh_token before it expires to get a new pair. Our token rotation test shows which old tokens keep working after a refresh, and that rotation cannot be turned off again.
xapp app-level tokens
App-level tokens start with xapp- and come from Basic Information in your app settings. They are for app-wide APIs, most often Socket Mode connections, not for posting messages.
Which token can set presence?
users.setPresence sets the calling user's presence to away or auto, so with a user token it changes the user's own dot; a bot token changes the bot's. No token can force a user to active. Code and fields are in our Slack presence API guide.
FAQ
Do Slack bot tokens expire?
Not unless you turn on token rotation; then access tokens expire after 12 hours and you refresh them. Without rotation, ours kept working until we deleted the app.
What are xoxc and xoxd tokens?
The web client's session token and cookie; see Slack xoxc and xoxd tokens.
Stop Jiggling Your Mouse.
Join hundreds of remote workers who never worry about their Slack status. Set it up once, stay green forever.
Related Articles
Slack Bot Scopes: The Scope Each API Method Needs, Measured on 44 Methods
We gave a Slack bot one scope, called 44 common Web API methods, and read the needed field of every missing_scope error. Then we added the scopes and called them again. The table shows which scope clears each method.
Slack File Size Limit: 1 GB Is Exactly 1,073,741,824 Bytes, Tested
We uploaded files of 50 MB, exactly 1 GiB and 1 GiB plus one byte to Slack through its upload API. The limit is 1,073,741,824 bytes, and a failed upload can still leave a broken file behind.
Slack Dark Mode: Where the Setting Is, and Which Custom Emoji Disappear
Slack's dark mode is under Preferences > Appearance > Color Mode, with Light, Dark and System. We switched modes in Slack web with three test emoji and measured which ones vanish.