
Slack Bot on Cloudflare Workers: Signature, 3-Second Ack, waitUntil
A Cloudflare Worker can answer Slack slash commands with no framework: verify the signature with WebCrypto, reply within 3 seconds, and finish slow work in ctx.waitUntil. We ran it under wrangler dev 4.163.0 on 17 November 2026 and timed each step.
A Slack bot fits in one Cloudflare Worker: verify the X-Slack-Signature header with WebCrypto, answer the slash command within 3 seconds, and do slow work inside ctx.waitUntil(), then post the result to the response_url. We ran the Worker below under wrangler dev 4.163.0 on 17 November 2026, put it behind a Cloudflare quick tunnel, pointed a test Slack app at it and sent real commands. The fast path answered in 13 ms, the follow-up arrived 4 seconds later, and the slow version failed with operation_timeout after about 3.4 seconds.
The Worker
No Bolt, no Hono, no npm packages at run time. Workers have crypto.subtle, so the HMAC check is a few lines:
const enc = new TextEncoder();

async function verifySlack(request, body, secret) {
  const ts = request.headers.get("x-slack-request-timestamp");
  const sig = request.headers.get("x-slack-signature") || "";
  if (!ts || Math.abs(Date.now() / 1000 - Number(ts)) > 300) return false;
  const key = await crypto.subtle.importKey(
    "raw", enc.encode(secret), { name: "HMAC", hash: "SHA-256" }, false, ["verify"]
  );
  const hex = sig.replace("v0=", "");
  const bytes = new Uint8Array(hex.match(/../g)?.map((h) => parseInt(h, 16)) || []);
  return crypto.subtle.verify("HMAC", key, bytes, enc.encode("v0:" + ts + ":" + body));
}

const sleep = (ms) => new Promise((r) => setTimeout(r, ms));

export default {
  async fetch(request, env, ctx) {
    const t0 = Date.now();
    const body = await request.text();
    if (!(await verifySlack(request, body, env.SLACK_SIGNING_SECRET))) {
      return new Response("bad signature", { status: 401 });
    }
    const verifyMs = Date.now() - t0;
    const form = new URLSearchParams(body);
    if (!form.get("command")) return new Response(null, { status: 200 }); // events and other payloads
    const text = form.get("text") || "";

    if (text.startsWith("slow")) {
      // The mistake: do the slow work before answering
      await sleep(4000);
      return Response.json({ text: "Done after 4 s (too late)" });
    }

    // The fix: answer now, finish the work in waitUntil
    ctx.waitUntil((async () => {
      await sleep(4000);
      const r = await fetch(form.get("response_url"), {
        method: "POST",
        headers: { "Content-Type": "application/json" },
        body: JSON.stringify({ response_type: "in_channel", text: "Report for " + text + " is ready (posted 4 s later from waitUntil)" }),
      });
      console.log("response_url", r.status, await r.text());
    })());
    console.log("ack after", Date.now() - t0, "ms, verify", verifyMs, "ms");
    return Response.json({ text: "Working on " + text + "..." });
  },
};
wrangler.toml holds only name, main = "src/index.js" and a compatibility_date. The signing secret goes in .dev.vars for wrangler dev and in wrangler secret put SLACK_SIGNING_SECRET for a deployed Worker. The line that returns early for anything without a command field matters: our first version crashed with TypeError: Invalid URL: null because the same URL also received Events API messages, which carry JSON and no response_url.
What we measured
| Step | Result |
|---|---|
| Unsigned POST | 401 in 27 ms |
| Signature check, first request | 4 ms (key import plus verify) |
| Signature check, later requests | Under 1 ms |
| Slash command answered | 200 in 13 ms, reply "Working on weekly-sales..." |
response_url POST from waitUntil, 4 s later | 200 ok, follow-up shown under the reply |
| Slow handler (4 s before answering) | Slackbot: /sg1117 failed with the error "operation_timeout"; the API call that ran the command returned operation_timeout after 3,361 ms; the Worker still logged 200 OK (4032ms) |
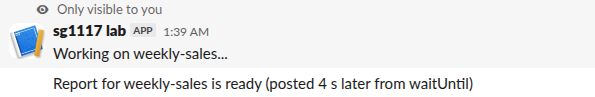
Slack gives a slash command about 3 seconds. After that it shows its own error to the person who typed the command, even if your Worker finishes and returns 200 later:
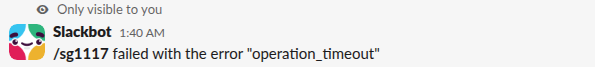
ctx.waitUntil() is the Worker way to answer first and keep working: the promise you pass keeps running after the response is sent. Socket Mode needs a long-lived WebSocket client, which is a poor fit for a request-driven Worker, so this setup uses HTTP request URLs.
Never appear "away" on Slack again
Cloud-based. No downloads. Works 24/7 even when your laptop is off.
Running it locally
npm install wrangler
npx wrangler dev --ip 0.0.0.0 --port 3000
cloudflared tunnel --url http://localhost:3000
Put the trycloudflare.com URL plus any path into the slash command's Request URL. Two things cost us time:
- In the
node:22-slimDocker image,wrangler devstopped withservice internet: TLS configuration: unexpected error: No CA certificates were loaded from the system. The fullnode:22image, which ships CA certificates, worked. wrangler devreloads on save (Local server updated and ready), so you can fix the Worker while the tunnel stays up.
Bolt, slack-edge or plain fetch
Bolt for JavaScript is built around Node's HTTP server and its Socket Mode client, and we did not try it on Workers. The slack-cloudflare-workers package from the slack-edge project is made for Workers, and its README shows a Bolt-like app.command(...) with a separate lazy listener for slow work. Hono also works as a router in front of the same code. We did not run those two here. For one or two slash commands, the plain Worker above is 48 lines with no dependencies to update.
If you need more than slash commands, the same Worker can take Events API calls (answer the url_verification challenge first, as our URL verification test shows) and button clicks. The signing secret check is the same in any runtime: HMAC-SHA256 over v0:timestamp:body.
FAQ
Can I call the Slack Web API from a Worker?
Yes. fetch("https://slack.com/api/chat.postMessage", ...) with Authorization: Bearer xoxb-... is a normal HTTP call. Store the token as a Worker secret.
Does waitUntil have a time limit?
Yes, Cloudflare limits how long work may continue after the response. Our 4-second job finished every time; check Cloudflare's current limits before you run long work there, or hand it to a Queue.
Why does my Worker get requests with no command? If Event Subscriptions or Interactivity use the same URL, those requests arrive too. Branch on the body type before you read slash command fields.
Stop Jiggling Your Mouse.
Join hundreds of remote workers who never worry about their Slack status. Set it up once, stay green forever.
Related Articles
Slack App Configuration Token: Generate, Rotate and Revoke
An app configuration token lets a script create Slack apps from manifests. We generated one, rotated it five times and tested it again 28 hours later.
Slack App Collaborators: Add, Remove and Transfer Ownership
Collaborators are the people who can edit a Slack app. We added and removed one on 20 November 2026 as a regular member of a test workspace, recorded who can be added and what Slack asks you to do after a removal, and wrote down the hand-over path Slack documents.
Slack Bolt Middleware: Global and Listener, Tested
Global middleware runs for every request and listener middleware for one listener. We ran both in Bolt for Python and Bolt for JavaScript on 20 November 2026 and logged what Slack did when next() was skipped: Python answered 404 and Slack sent the event again.